
Anti-Intrusion (IPS)
Efficient, Scalable Intrusion Prevention System Designed for the Edge.
Get in touchOVERVIEW
Embedded-First Threat Prevention Built on Deep Packet Inspection
Embedded-First Threat Prevention Built on Deep Packet Inspection
Lionic IPS is designed from the ground up for embedded systems. Unlike oversized engines made for servers, it delivers efficient, real-time threat prevention without exhausting system resources. By inspecting actual payloads instead of just IP addresses, it detects real attacks from malware to brute-force attempts, with smart acceleration and weekly rule updates.
BENEFITS AND FEATURES
Flexible Deployment Scenarios Powered by DPI-Based Intrusion Detection

Packet-Level Attack Detection
Lionic IPS inspects actual packet payloads to detect real-world attacks. This ensures threats are caught even when IP-based filtering fails.

Optimized for Embedded System
Designed with efficiency in mind, our IPS runs smoothly on resource-limited gateways. Perfect for home routers and CPE devices.

Self-Owned Rule Database
We maintain over 8,000 IPS rules across key threat categories. Signature files are updated weekly with no third-party dependency.

Protocol Anomaly Detection
Detects abnormal patterns in L2 to L7 headers, such as malformed TCP flags or corrupted URLs. Catches threats that evade traditional signatures.

DoS and DDoS Resilience
Instantly blocks DoS bursts by rate-limiting abnormal connections. For DDoS, it intelligently preserves resources for valid traffic.

Brute-Force Login Defense
Monitors failed login attempts across services. Stops automated attacks before they compromise local credentials.

Legacy System Protection
Protects older devices that cannot be updated due to business or operational constraints. Especially useful in industrial or medical networks.

Dynamic Scan Control
Adjusts scan depth based on session behavior. This keeps performance high while maintaining strong protection.

Threatpedia Integration
Each alert links to detailed analysis with CVEs, impact, affected products, and mitigation advice. Helps admins respond quickly and accurately.
FAQ
Built-in Intelligence for Real World Threat Defense
USE CASES
Use Cases for Intrusion Prevention System
Mitigate Service Disruption During Burst or Targeted Attacks
DDoS attacks remain a persistent threat for businesses and service providers alike. While full prevention requires upstream filtering, Lionic IPS includes smart mechanisms to mitigate the impact on-premise by prioritizing legitimate connections and applying traffic shaping to minimize service downtime.
Strengthen Defense Layers in Enterprise Networks
Modern businesses face constant threats from malware, unauthorized access attempts, and lateral movement inside the network. Lionic IPS provides a real-time layer of protection by detecting known attack patterns, suspicious behavior, and protocol anomalies, helping stop threats before they escalate. It integrates smoothly with other network protections to form a comprehensive security posture.
Offer Value-Added Protection Services for ISPs
ISPs can deploy Lionic IPS on CPE devices to provide silent, always-on intrusion prevention to their subscribers. It helps block brute-force attacks, port scans, and known exploits without requiring user intervention, reducing abuse complaints and customer churn while offering premium upsell opportunities.
Protect Critical Infrastructure with Outdated Systems
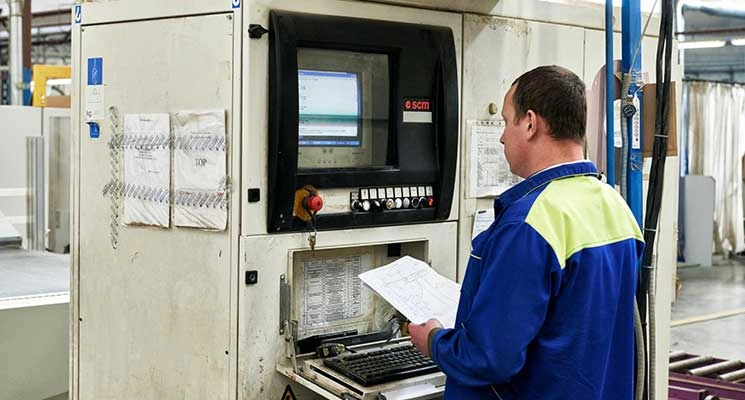
In manufacturing, medical, or industrial environments, legacy computers and controllers often run operating systems or software that cannot be updated or replaced. Lionic IPS helps secure these devices by detecting exploits targeting old vulnerabilities, offering practical protection without disrupting essential operations. This ensures extended equipment lifecycles while reducing risk exposure from known threats.
Secure Edge Devices in Smart Home and IoT Ecosystems
Smart devices are often the weakest link in home networks, lacking proper security updates. Lionic IPS guards against attempts to exploit these endpoints by analyzing the traffic flow at the gateway level, catching common attack patterns before they compromise connected devices.